
Barracuda SOC Powered XDR
Level Up Your Defence with Barracuda Managed XDR’s Award-Winning SOC
The superpower of Managed Detection and Response
The Security Operations Centre (SOC) is the relentless guardian behind Barracuda Managed XDR. Staffed by elite cybersecurity professionals who live and breathe threat defence, Barracuda’s SOC operates 24/7/365, blending human expertise with advanced AI and automation to deliver security and peace of mind that no tool or platform alone can match.
SOC in action: real-world case files
Barracuda’s SOC is battle-tested. The SOC Case Files series offers a window into the daily reality of defending organisations against sophisticated threats. Each story is a detailed, technical account of how the SOC detects, contains and eradicates attacks.

Akira ransomware neutralised
- Stopped Akira ransomware by detecting abuse of the organisation’s own remote monitoring and management (RMM) tools
- Identified “Living off the Land” (LotL) tactics and acted within minutes to isolate the threat before encryption
- Contained fast using custom detection rules and rapid-response playbooks
RansomHub ransomware exploit blocked
- Attackers exploited a FortiGate zero-day giving them admin access
- Spotted suspicious logins and RansomHub deployment attempts across multiple servers, even without the full Barracuda MDR suite in place
- Quarantined compromised devices, stopped the attack, and guided recovery to help the organisation harden its environment

Impossible travel attack
- Detected “impossible travel” when the same credentials were used within minutes from two distant locations
- Automatically suspended the account to prevent unauthorised access and stop the breach in progress
- Followed up directly with the organisation by phone to ensure awareness and next steps, all within minutes
These stories are just a sample. The SOC’s case files are a living record of how Barracuda’s experts outpace and outmanoeuvre attackers every day.
SOC structure:
Six levels, five teams, one mission
Barracuda’s SOC is a group of dedicated cybersecurity experts. It is a mature, global, multi-tiered operation, employing a follow-the-sun approach. More than just a single room of analysts, the SOC is a distributed and coordinated network of specialised teams, each with a distinct focus, so that your security never sleeps. Combined, the SOC ensures every aspect of your business and its entry points are protected. This hierarchy ensures every alert, every anomaly and every customer concern is handled by the right expert, at the right time, anywhere in the world.
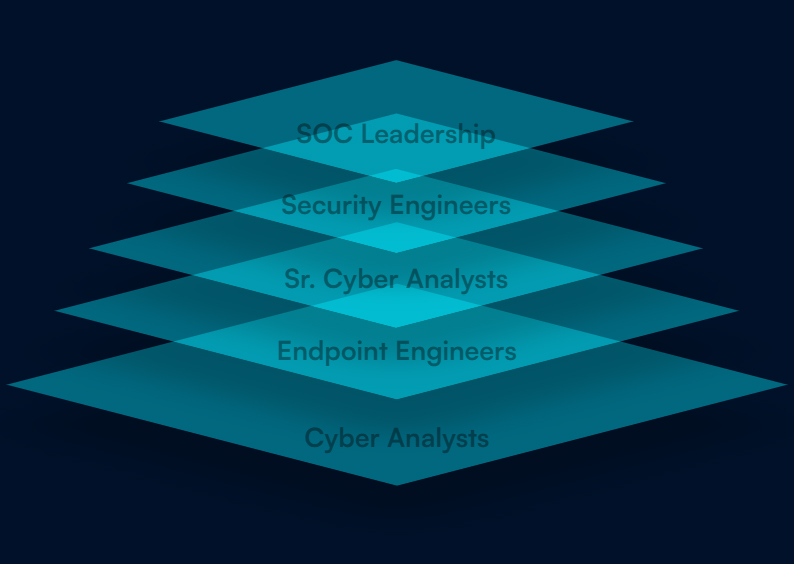
Cyber Analysts. Blue Team - Detect Attacks
- Defensive Security
- Protect Systems and Data
- Incident Guidance
Endpoint Engineers. Green Team - Endpoint Security
- Endpoint Protection Management
- Device Policy Management
- Attack and Defend Exercises
- Malware Analysis
- Threat Hunting
- Research and Development
Sr. Cyber Analysts. Purple Team - Improve Efficiency
- Collaborative Security
- Improve both Red/Blue Team
- Workflow Automation
- Process Enhancements
- Customer Escalations
- Emerging Threats
Security Engineers. Red Team - Exploit Weaknesses
- Adversary Simulation
- Use Case Development
- Attack Detect Methods
- Threat Intelligence
- Threat Hunting
- New Threats R&D
SOC Leadership. White Team
- Quality Assurance
- Compliance
- Process
SOC best practices and continuous improvement
Barracuda’s SOC is built on best practices that go beyond industry standards:

Runbooks and playbooks
Proprietary, SOC-authored procedures ensure consistent, rapid and effective response to every alert.

Continuous training
Analysts participate in red/blue/purple team exercises and hackathons, and commit to ongoing education to stay ahead of evolving threats.

Metrics and outcomes
The SOC measures mean time to detect, mean time to respond, SLA performance, and customer satisfaction, constantly refining processes to deliver better outcomes.
Relentless threat hunting and proactive defence
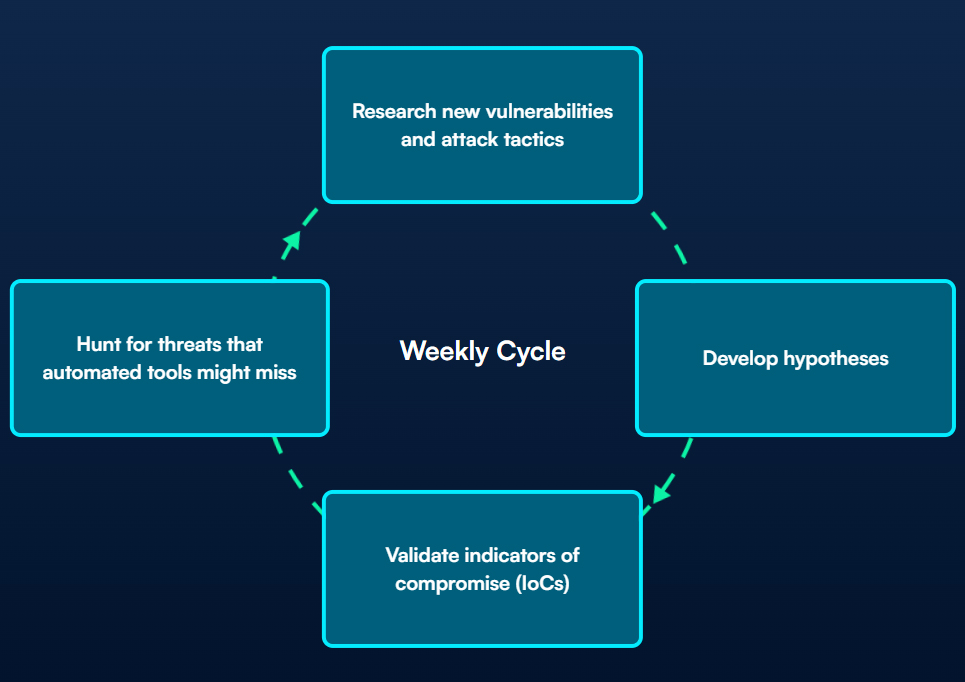
Threat hunting at Barracuda is a continuous, foundational discipline. Within Barracuda’s SOC, this is formalised as the Emerging Threats Process: a structured, weekly cycle where analysts research new vulnerabilities and attacker tactics. They develop hypotheses, validate indicators of compromise and proactively hunt for threats that automated tools might miss. This ongoing exercise is a core differentiator for Barracuda’s SOC and a testament to its commitment to staying ahead of adversaries.
AI and human judgment — together
The SOC works from one of the industry’s largest threat intelligence databases, comprising 11 billion indicators of compromise (IoCs) and growing every day. It is bolstered by a continuously learning AI engine and hundreds of machine learning-enhanced detection rules aligned to the MITRE ATT&CK framework.
But technology alone is not enough. The SOC’s real power is in how it combines these tools with human intuition, creativity and experience. Analysts go above and beyond chasing alerts — building context, correlating signals, validating threats, and ensuring that nothing is missed while every response is precise.
Global, always on, and award winning
Follow-the-sun model
With SOC analysts in the US, EMEA, APAC, and beyond, Barracuda delivers 24/7/365 coverage so that your security never sleeps.
Industry recognition
Barracuda Managed XDR and its SOC have been named Best SecOps Solution (Tech Ascension Awards), XDR Solution of the Year (CyberSecurity Breakthrough Awards) and have won multiple Global InfoSec Awards for innovation, service and vision.
Customer impact
The SOC’s work is reflected in customer success webinars, testimonials and case studies, with organisations praising the team’s responsiveness, expertise and ability to stop threats that others miss.
How Barracuda SOC delivers on SLAs
Barracuda Managed XDR’s SOC is built on a foundation of clear, measurable Service Level Agreements (SLAs) that ensure customers receive rapid, expert response to every security alert. Barracuda SLAs are designed to prioritise what matters most—speed, reliability and peace of mind.

Three-tiered SLA structure
High risk alerts
- Response within 20 minutes
- For critical threats, Barracuda SOC initiates a phone call and email/ticket integration — typically within minutes — to ensure immediate action.
Medium risk alerts
- Response within 1 hour
- Timely email/ticket updates keep your team informed and protected.
Low risk alerts
- Response within 8 hours
- Routine alerts are handled efficiently, with updates delivered via email/ticket integration.

SOC performance: proven results
Alert SLA achievement
Barracuda SOC meets or exceeds SLA targets for alerts 96+% of the time.
Call SLA achievement
For phone calls related to high-risk alerts, Barracuda SOC regularly achieves 90+% SLA compliance rate.

Why it matters
Rapid response
Barracuda SOC’s commitment to these SLAs ensures threats are contained before they escalate — minimising risk and business disruption due to downtime.
Continual improvement
Barracuda continuously tracks and analyses monthly SLA achievement metrics, driving faster response times and an ever-better customer experience.
Accountability
SLAs are more than promises — they’re transparent, measurable outcomes that hold Barracuda SOC to the highest standards of operational excellence.
Barracuda’s SOC:
People + process + technology
What truly sets Barracuda’s SOC apart is the synergy of world-class talent, proven processes and cutting-edge technology. The SOC is committed to giving customers peace of mind from a security partner they can trust.
The SOC is Barracuda’s superpower.
- It’s the difference between a checkbox and real protection.
- It’s the difference between generic alerts and actionable insight.
- It’s the difference between reactive defence and proactive cybersecurity leadership.
Technical spotlight: Detection rule engineering
The Green Team in Barracuda’s SOC specialises in authoring and optimising STAR rules—bespoke detection logic deployed across endpoints to rapidly identify and contain sophisticated threats, including ransomware.
This continuous rule engineering ensures customer environments are proactively safeguarded from high-impact incidents.
Schedule your Managed XDR demo
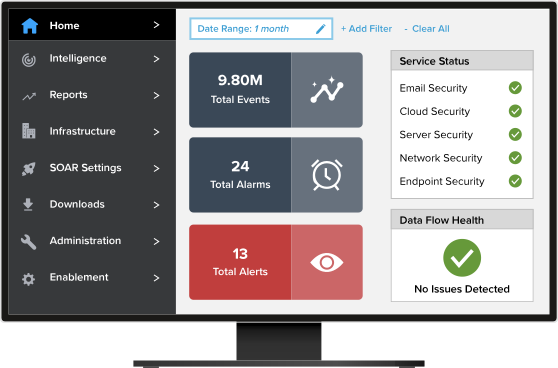
Get a personalised product demo with a Barracuda cybersecurity expert.
What is covered in the demo:
- Overview of the threat types Barracuda monitors.
- Identifying the top risks in your organisation.
- How Barracuda’s 24×7 SOC team works.
- Integrating XDR into your infrastructure.
- How Barracuda accelerate threat response times.